ESC1–ESC16 research and attack-path catalog.
Briefing
Not a landing page. A work file.
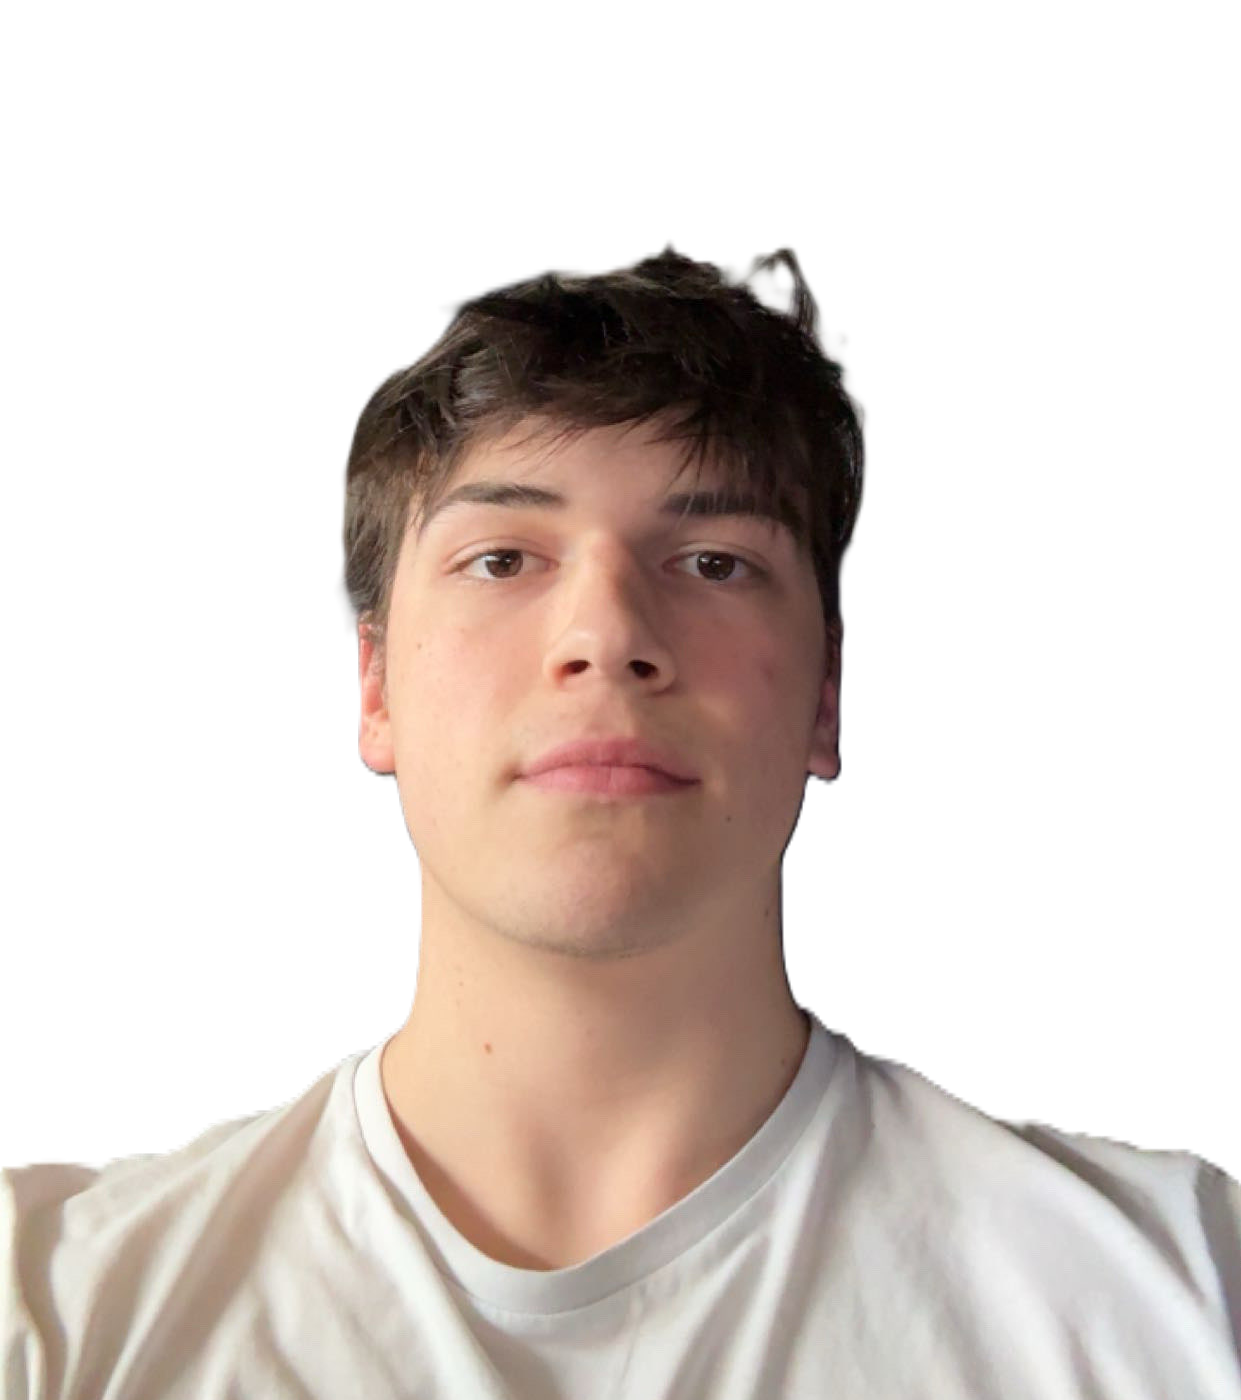
I am a cybersecurity graduate from Thomas More University of Applied Sciences with a focus on offensive security, infrastructure engineering, and cloud-native technologies.
My work is practical: build the environment, break it, measure what defenders can see, then turn the result into something reusable. The main focus areas are Active Directory exploitation, AD CS abuse paths from ESC1 through ESC16, Wazuh detection engineering, cloud infrastructure, and automation.
Wazuh, Shuffle, VirusTotal, IRIS, active response.
60+ hours across AD, gMSA, WSUS, ESC13, and RODC labs.
Selected participant in Belgium's national ethical hacking initiative.
Open Case Board
Selected work, arranged by signal.
AD CS Security Research
14-week offensive security research internship producing a complete ESC1–ESC16 vulnerability catalog, stealth-focused enumeration tooling in PowerShell and Python, Wazuh + Sysmon detection analysis, and a cross-domain trust exploitation case study.
Automated SOC Defense Loop
End-to-end detection-to-response workflow with Wazuh, Shuffle, VirusTotal, IRIS, and endpoint active response.
Ethical Hacking & Pentest Reporting
Team-led penetration test with AD-focused attack tracks, client coordination, and final reporting.
HTB Mastery & Active Directory Labs
Logging, Silentium, Garfield, Ping, Ligolo-ng, gMSA abuse, ESC13, and Ludus lab work.
The Cyber Dojo
Adversarial infrastructure and penetration-testing lab design.
Capability Ledger
Tools and techniques.
Offense
Internal network pentesting, AD exploitation, AD CS abuse, privilege escalation, Kerberos trust abuse, web application security, BloodHound, Rubeus, Impacket, Mimikatz, Burp Suite, and Nmap.
Infrastructure
Linux administration, Windows Server, AD DS, DNS, PKI, Docker, Kubernetes, VMware, VirtualBox, Wazuh SIEM/XDR, and SOAR automation.
Cloud & Code
AWS ECS, ECR, VPC, IAM, Python, FastAPI, PowerShell, Bash, and infrastructure-as-code foundations.
Detection
AD CS attack simulation, detection engineering, Wazuh custom rules, threat analysis, VirusTotal enrichment, and incident response workflows.
Timeline
Background record.
Internship
Cybersecurity Intern · Refracted Security
AD CS research, stealth enumeration tooling, Wazuh detection gap analysis, and cross-domain trust exploitation.
Recognition
Hack The Government Belgium
Selected participant in the national ethical hacking initiative coordinated by the Belgian Centre for Cybersecurity.
Education
Professional Bachelor · Electronics-ICT, Cloud & Cybersecurity
Thomas More Hogeschool, Geel. Specialization track: Ethical Hacking.
Internship
ICT Helpdesk Intern
Phone infrastructure mapping, laptop staging, and automated label-printer workflow.
Outside Record
LoForLife and long-term discipline.
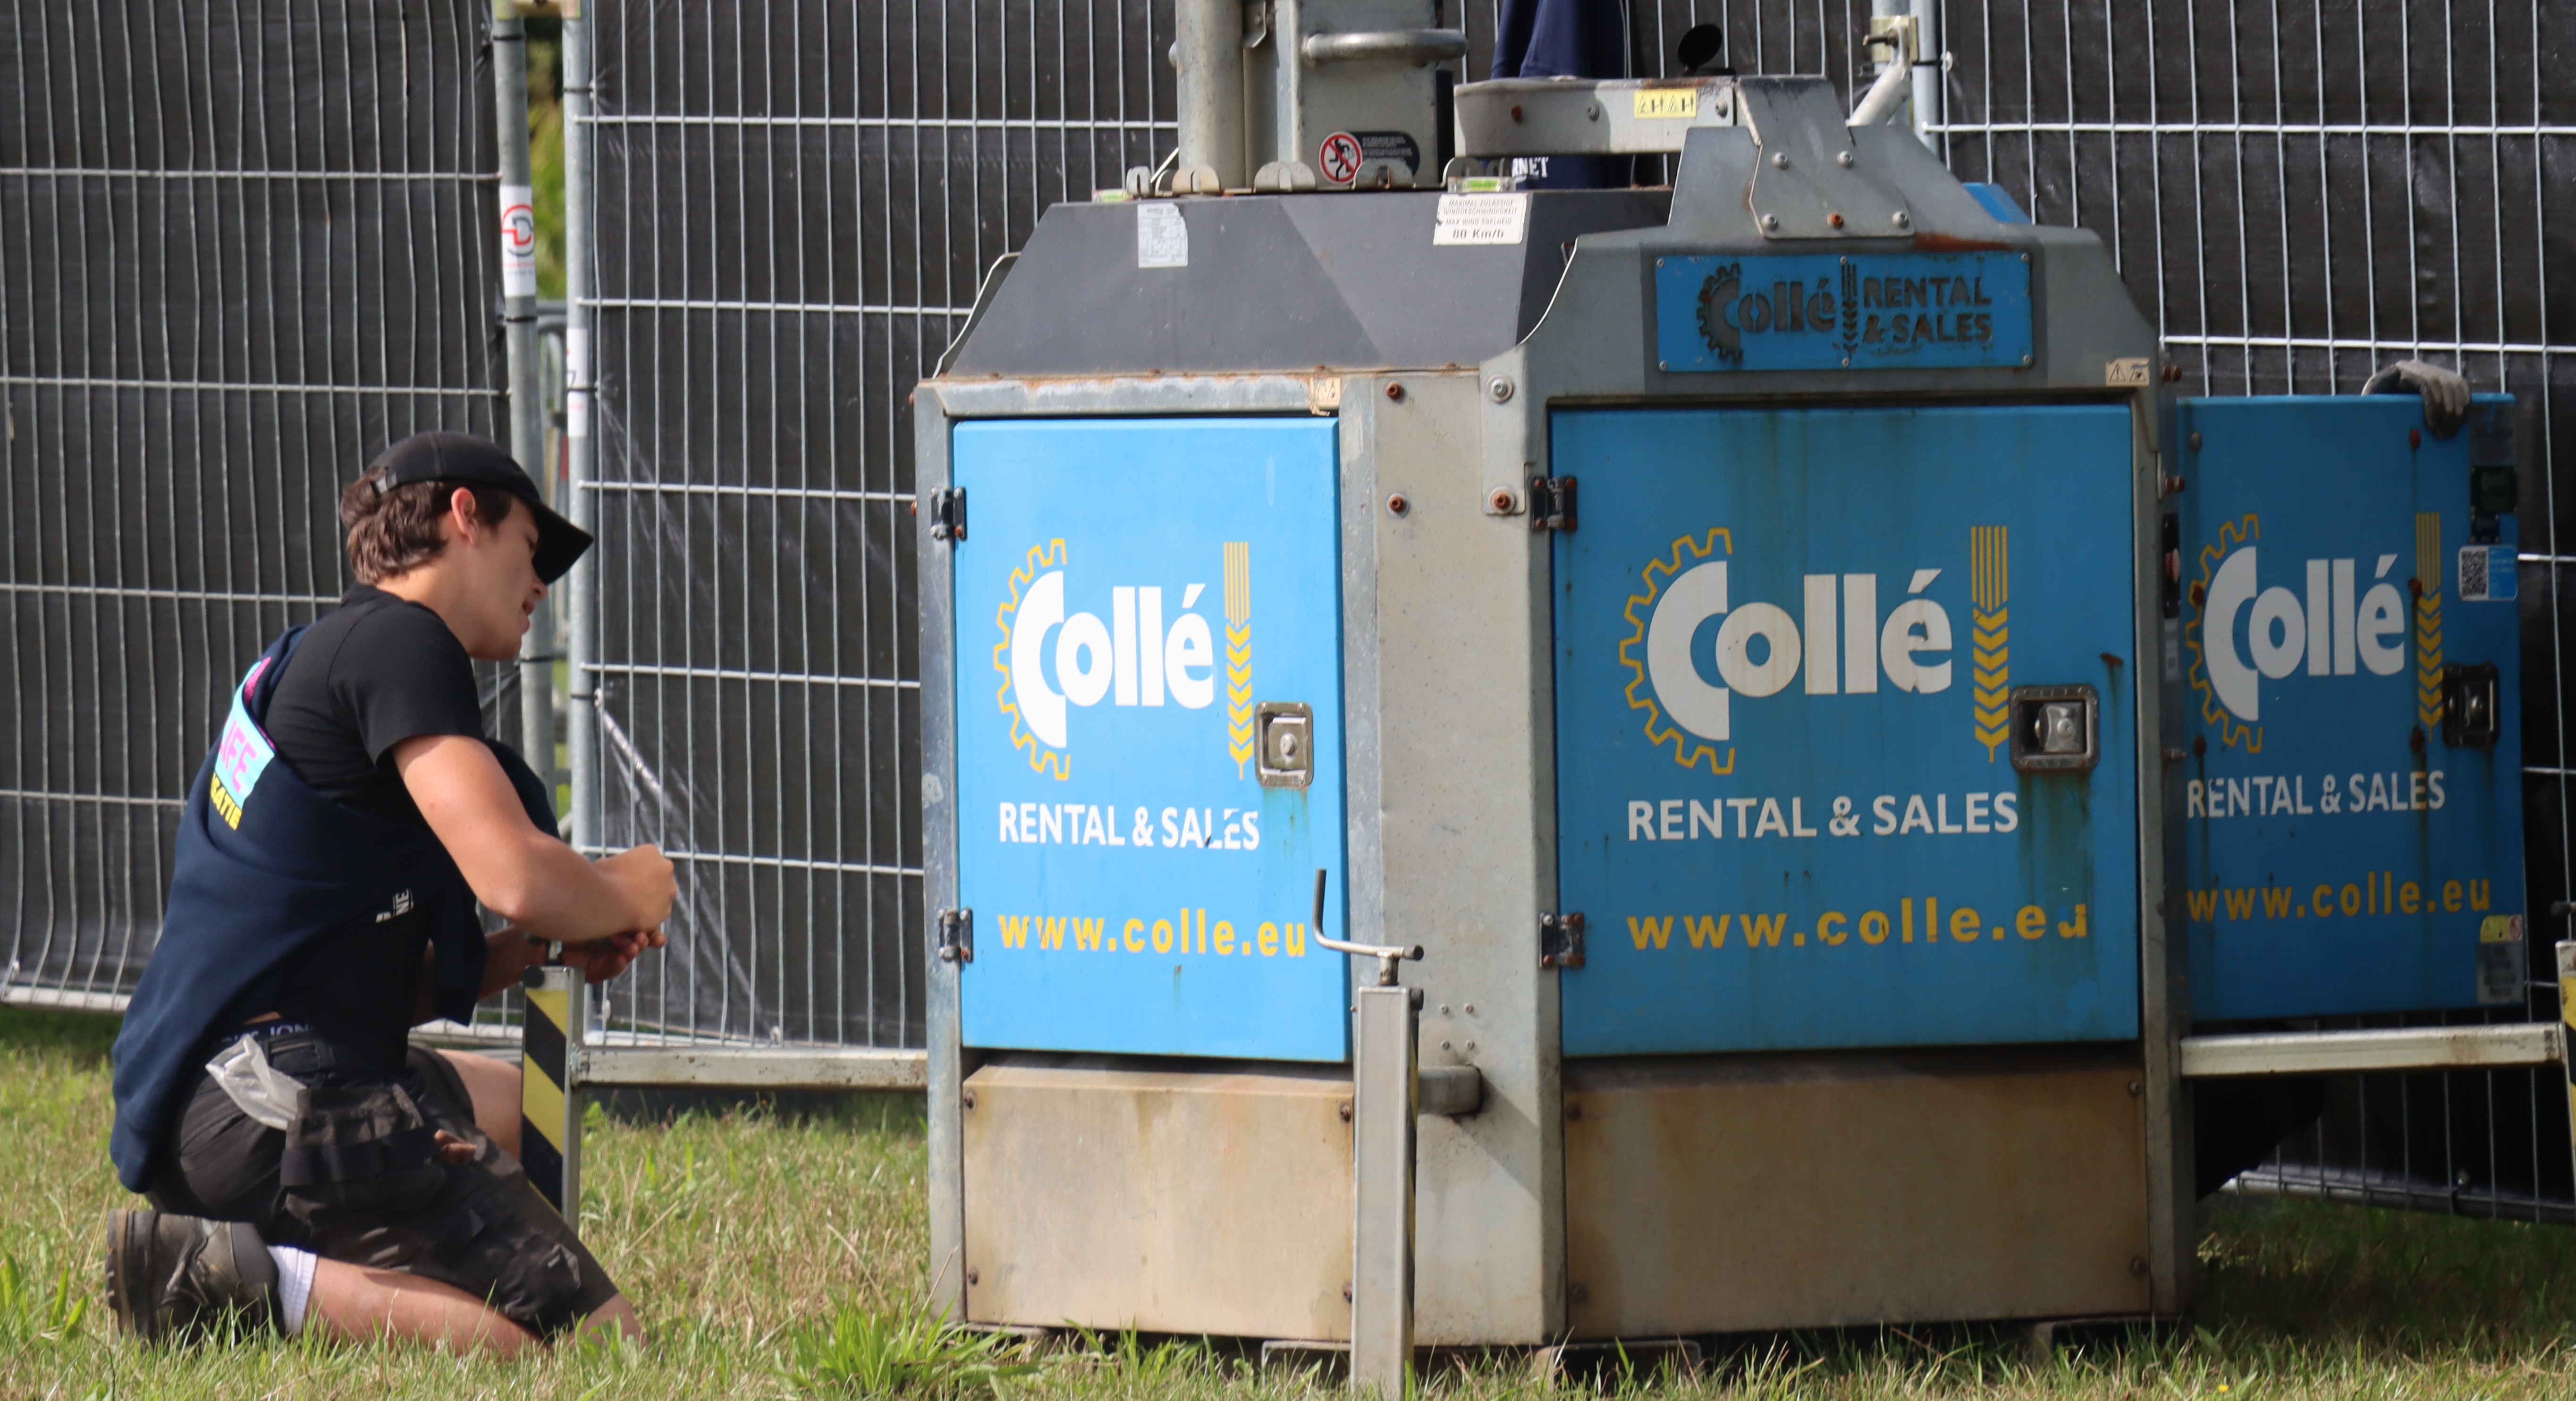
Outside of cybersecurity, I co-organize LoForLife, a volunteer-run festival benefiting ALS research and attended by around 12,000 people annually. Setup, breakdown, and stagehand work shaped how I handle pressure, coordination, and practical problem-solving.
Strength training supports the same mindset: consistency, goal setting, discipline, resilience, and slow improvement over time.